


The GRC Maturity Model: How Mature is Your GRC Program?
White Papers25 Sep 2026
Sponsored by Hyperproof


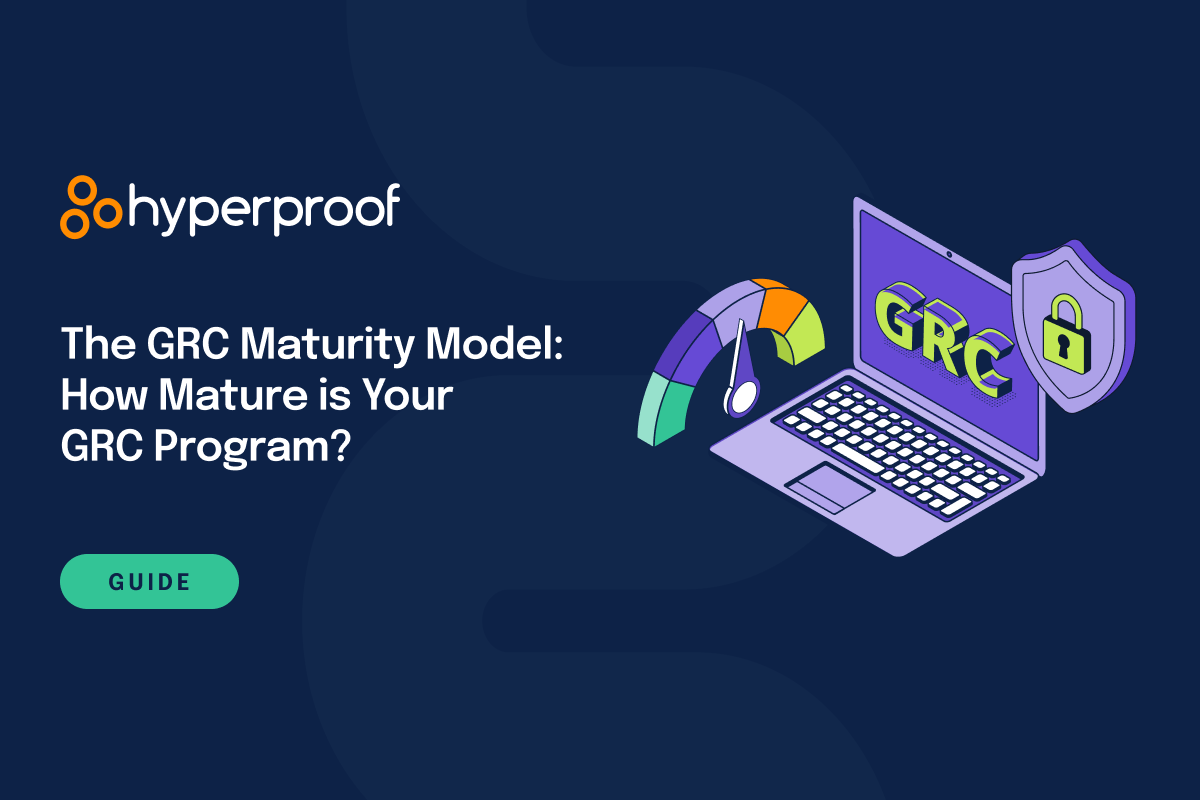
The Hyperproof GRC Maturity Model gives organizations a vendor-agnostic roadmap for evaluating and advancing their Governance, Risk, and Compliance program, built with input from CISOs, security leaders, and GRC practitioners.
This guide breaks down five progressive maturity levels — Ad Hoc, Fragmented, Standardized, Integrated, and Optimized — across all three GRC pillars, so your team can see exactly where it stands today.
Access the guide to:
- Pinpoint your program’s current maturity level across Governance, Risk, and Compliance
- Identify the highest-impact next steps instead of guessing where to invest
- Benchmark your program against a vendor-neutral, practitioner-built framework
Download Now
Related Content
2024 Mid-Year Consumer Outlook from NielsenIQ and GfKSPONSORED ARTICLE
2026 ESG Metrics Guide: What Investors Are TrackingSPONSORED ARTICLE
5 Emerging Risk that Matter More NowSPONSORED ARTICLE
6 Requirements for Agentic AI-Ready SystemsSPONSORED ARTICLE
90 Day Roadmap for Implementing Skills-Based HiringSPONSORED ARTICLE
A 5-Point Blueprint for Evolving Risk & Compliance ProgramsSPONSORED ARTICLE
Supply Chain Talk
view all
Wednesday, 21 Oct 2026
Why unified, AI-powered supply chains are pulling ahead - and what the rest risk losing
Wednesday, 11 Nov 2026
Connecting the supply chain - Why the yard matters more than ever
Winston House, 3rd Floor,
Units 306-309, 2-4 Dollis park,
London, N3 1HF
020 8349 4363
© 2026, Lyonsdown Limited. teiss® is a registered trademark of Lyonsdown Ltd. VAT registration number: 830519543